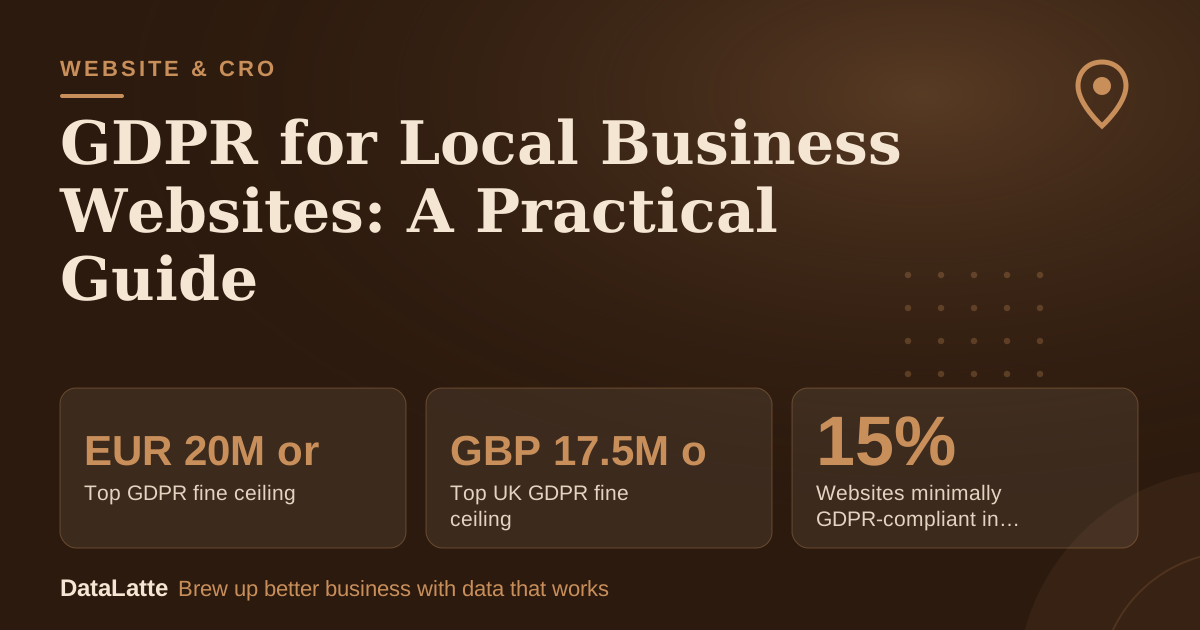
A local business website that handles personal data of people in the EU or UK needs five things to follow GDPR: a privacy notice that says what you collect and why, prior opt-in consent for non-essential analytics and advertising cookies, forms that collect only what you need, a way to handle data requests and objections, and a plan to report a breach within 72 hours where the conditions apply. The maximum GDPR fine is EUR 20 million or 4% of worldwide annual turnover, whichever is higher. This guide explains each step in plain language. It is general information, not legal advice.
→
Top GDPR fine ceiling
Adwave, secondary
→
Top UK GDPR fine ceiling
Adwave, secondary
→
Websites minimally GDPR-compliant in a 2025 study
Adwave citing an ACM study, secondary
→
Breach report window where conditions apply
Adwave, secondary
See Sources at the end of the article. Cards marked Assumption are examples, not results.
Does GDPR Apply to My Local Business?
Size and location on their own do not decide it. A page on the
Adwave cookie banner guide (secondary) notes that the UK GDPR carries its own ceiling of GBP 17.5 million or 4% of worldwide annual turnover, whichever is higher. The
Adwave guide to CAN-SPAM and GDPR (secondary) makes the scope point directly: GDPR can become relevant when the data belongs to an EU resident, regardless of where the business is located.
So a café, salon or groomer in Toronto, Sydney or Leeds can still be in scope if its forms or ads collect data from people in the EU. The test is whose data you hold, not where your shop sits.
The regulation has been in force since May 25, 2018. A 2019 survey cited by Mailforge found that over 50% of European small businesses felt uncertain about key compliance requirements. If that describes your team, you are not alone, and the rest of this guide is a practical starting point.
What Does Your Site Collect?
Start by listing every place your site touches personal data. A contact form, booking widget, newsletter box, analytics script, live chat, embedded map and social media pixel each count. Maps are easy to forget. An
embedded Google Maps setup is part of your site, so it belongs on the same list.
The
guide to AI agents for appointment booking shows why this matters for bookings. Once a tool captures names, phone numbers or appointment details, that data is personal data, and it needs a home in your records and your notice.
You cannot write an accurate privacy notice or set cookie rules until this list exists. Keep it short and review it when you add a new tool.
When Do You Need Cookie Consent?
Under the EU framework, prior opt-in is required for non-essential analytics and advertising cookies, subject to applicable exemptions. The
Adwave cookie banner guide (secondary) also says Global Privacy Control is not a general substitute for the consent process under EU GDPR, ePrivacy or UK PECR. A browser signal does not replace a consent banner.
The same page cites a 2025 Association for Computing Machinery cross-country study that found only 15% of websites were minimally GDPR-compliant. That number is a reason to check your own site, not to assume you are in the majority.
Banner design matters too. A
2024 review of 642 subscription websites and apps (secondary), carried out by ICPEN with the FTC and the Global Privacy Enforcement Network, found that nearly 76% used at least one possible dark pattern. A reject button that is hard to find is a pattern regulators look for, so give accept and reject equal prominence.
Yes, when they involve EU residents. The Adwave guide states that a lead form, remarketing audience, CRM entry and follow-up campaign can all fall in scope if they involve data from EU residents. Treat each one as a data flow with its own purpose and retention.
Email needs its own rules. The same guide explains that CAN-SPAM is a U.S. law focused on commercial email and can carry penalties on a per-email basis. A StackAdapt article on B2B email automation says GDPR and CAN-SPAM require built-in consent management, unsubscribe logic and data governance in the email stack. In practice, that means an unticked signup box, a visible unsubscribe link and a record of consent for each list.
A 2025 Unspam benchmark cited by
Adwave on cold email compliance (secondary) found that 49% of emails complied with GDPR, even though global deliverability health scored 86 out of 100. Good deliverability does not mean good compliance. When you compare
email tools for small businesses, check consent and unsubscribe features first.
Which Vendors Need Checking?
Most local sites run on third-party tools, and each one that handles personal data on your behalf needs review. Vendor pages often state GDPR support. ElevenLabs says its data is encrypted in transit and at rest, with support for SOC 2, HIPAA and GDPR compliance, and offers Regional Data Residency and Zero Retention modes. MindStudio says its platform includes GDPR compliance.
These are product claims, not your contract. Ask each vendor for its data processing terms, check which data residency and retention settings apply to your plan, and save copies. If you use an AI agent for
customer service on your site, the same check applies to chat transcripts.
What Are the Fine Limits?
The GDPR ceiling is EUR 20 million or 4% of worldwide annual turnover, whichever is higher. The UK GDPR ceiling is GBP 17.5 million or 4%, whichever is higher. These figures are maximums. Regulators set fines case by case, and small businesses rarely face the top tier. Still, the ceilings show which failures are treated as serious.
A StackAdapt article on CCPA and GDPR states that companies in breach can be fined up to 4% of annual global revenue or 20 million euros. Adwave repeats the same ceiling. Both are secondary, so check the regulator's own text before you rely on exact wording.
Compliance also has a commercial side. A StackAdapt article reports that adhering to privacy regulations like GDPR avoids legal penalties and strengthens brand credibility. That is a vendor view, but it fits how customers judge a local business that asks for their data.
What Do You Do If Data Leaks?
The Adwave summary of GDPR says a discovered breach must be reported to regulators and affected individuals within 72 hours where the reporting conditions apply. The clock starts when you become aware of the breach, so you need a plan before one happens.
Here is a worked timeline. All times and tools are assumptions for an imaginary salon:
- Assumption: the salon's booking-tool login is found exposed on Monday at 09:00, and the owner confirms it that morning.
- Assumption: the 72-hour window therefore closes on Thursday at 09:00, the latest point for a report where reporting applies.
- Assumption: the owner writes down the time of awareness, the data involved and the steps taken from the first hour.
Prepare a one-page plan. Name the person who decides, store the login and vendor contacts somewhere the team can reach, and keep a list of which tools hold customer data. A lost phone with a booking app open is a breach, and so is an email sent to the wrong list.
What Should You Check Before Launch?
Use this checklist as a working plan. It is an original sequence, not a legal test:
- List every tool on the site and the personal data each one touches.
- Set non-essential analytics and advertising cookies to load only after prior opt-in, unless an exemption applies.
- Check that Global Privacy Control signals are not the only consent step.
- Make accept and reject options equally visible on the banner.
- Keep forms to the fields you need, and link your privacy notice beside each one.
- Add an unsubscribe link to every marketing email and record the consent behind each list.
- Collect vendor data processing terms and save them.
- Write a breach plan with a named decision maker and the 72-hour clock.
The table below is a worked audit for a salon website. Every row is an assumption, to show the method.
| Tool on site (assumption) | Personal data it touches (assumption) | First check |
|---|
| Booking widget | Name, phone, service chosen | Notice linked, vendor terms saved |
| Contact form | Name, email, message | Only needed fields kept |
| Newsletter signup | Email address | Unticked box, unsubscribe link |
| Analytics script | Device and page data | Prior opt-in if non-essential |
| Social media pixel | Browsing activity | Loads only after consent |
Confirm each row against the regulator's current guidance, or ask a data protection adviser, before you rely on it.
FAQ
Does GDPR apply to a small business outside Europe?
It can. The Adwave guide says GDPR can become relevant when the data belongs to an EU resident, regardless of where the business is located. Check whether your forms, ads or email lists collect data from EU residents.
What is the maximum GDPR fine?
The ceiling is EUR 20 million or 4% of worldwide annual turnover, whichever is higher. The UK GDPR ceiling is GBP 17.5 million or 4%, whichever is higher. These are maximums, not typical fines.
Do I need a cookie banner?
You need prior opt-in before non-essential analytics and advertising cookies, subject to applicable exemptions. A Global Privacy Control signal is not a general substitute for that consent under EU GDPR or UK PECR.
How fast must I report a breach?
Within 72 hours where the reporting conditions apply. The clock starts when you become aware of the breach, so record that time.
Sources
Want a website that collects leads and stays compliant?
Book a free audit and we will review your forms, cookies and tools against this checklist.
Free for local businesses
Want this applied to your business?
I'll review your Google presence, local SEO, and ad accounts — and send you a specific action plan within 48 hours. No pitch, no pressure.