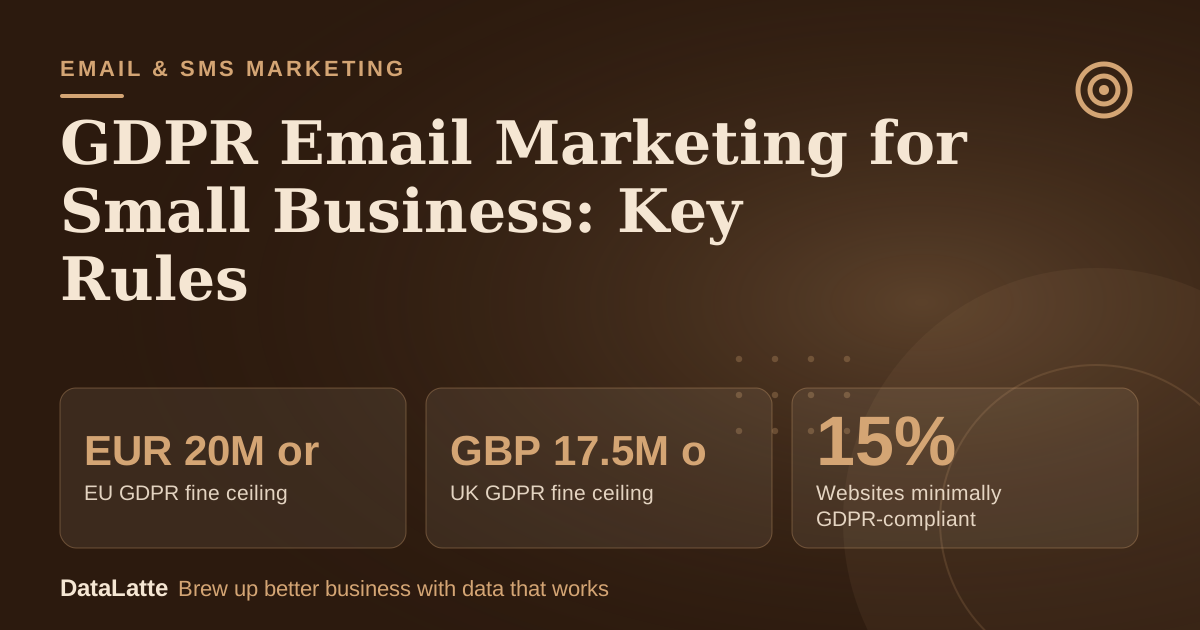
GDPR-compliant email marketing for a small business starts with explicit opt-in before you send marketing email to EU residents. The EU GDPR fine ceiling is EUR 20 million or 4% of worldwide annual turnover, whichever is higher, and the UK GDPR ceiling is GBP 17.5 million or 4% on the same basis (
adwave, cookie banner compliance). Your email stack also needs built-in consent management, unsubscribe logic and data governance (
StackAdapt). This guide covers the practical rules for newsletters and offers. It is general information, not legal advice, so check your national regulator's live guidance.
→
EU GDPR fine ceiling
Higher of the two, per adwave
→
UK GDPR fine ceiling
Higher of the two, per adwave
→
Websites minimally GDPR-compliant
2025 ACM cross-country study, secondary via adwave
→
Emails that complied with GDPR
2025 Unspam benchmark, secondary via adwave
See Sources at the end of the article. Cards marked Assumption are examples, not results.
What Does GDPR Require Before You Email Someone in the EU?
GDPR requires explicit opt-in consent before marketing emails are sent to EU residents (
adwave, behavioral email triggers). A subscriber who never agreed to marketing is not a list member you can email, even if you already hold their address from a booking or purchase.
Consent is only one part of the setup. Industry guidance on email stacks says GDPR, CAN-SPAM and evolving privacy rules call for built-in consent management, unsubscribe logic and data governance (
StackAdapt). For small businesses this means your sign-up form, your email platform and your unsubscribe process should be set up together, not patched later.
The same logic applies to abandoned cart emails. For EU recipients, one guide says a clear opt-out must appear in every single email sent (
adwave, abandoned cart emails). Build that link into your template so no campaign goes out without it.
Guidance also treats names, email addresses, tracking pixels, lead forms and direct messages as personal data you should document (
adwave, social media content audit). Any list built from social lead forms or contest entries falls under the same consent rules.
How Big Could a Fine Get for a Small Business? (Worked Example)
The fine ceiling is the higher of a fixed amount and a percentage of turnover, so the fixed amount is what matters for most small firms. All inputs below are assumptions.
Assume annual turnover of EUR 300,000 (assumption). Four percent of that is EUR 12,000. The higher of EUR 20 million and EUR 12,000 is EUR 20 million, so the EUR 20 million figure is the ceiling that applies.
The percentage only takes over above a threshold. Solving 4% of turnover = EUR 20 million gives turnover of EUR 500 million. Any business below that level faces the EUR 20 million ceiling under the EU rule. For the UK rule, GBP 17.5 million divided by 4% gives GBP 437.5 million, so the UK fixed figure applies below that turnover.
The ceiling is a maximum, not an expected penalty. The figure tells you why a small list of unconsented addresses is a serious risk, even though a regulator would weigh many factors before setting any amount.
What Are the Rules for US Senders Under CAN-SPAM?
CAN-SPAM is a U.S. law focused on commercial email. It regulates how a business sends promotional messages, not every way a business collects or stores customer data (
adwave, CAN-SPAM and GDPR). A US business emailing only American customers is mainly under this law.
Penalties can be assessed per email, so one flawed campaign sent to a large list multiplies the exposure. The same guidance recommends adding a valid physical postal address to every marketing email footer and warns against buying or scraping lists, recommending permission-based lists instead.
Mailchimp's benchmark guidance states that businesses must comply with anti-spam laws such as the CAN-SPAM Act in the United States and the GDPR in the European Union (
Mailchimp). If your list mixes US and EU addresses, you need both rule sets. The
SMS vs email guide covers channel choice, but the consent rules above apply to both channels.
Does Strict Opt-In Consent Affect Results?
Consent rules are not only a cost. One secondary summary, citing Hustler Marketing, says stricter GDPR-style opt-in consent can improve email open rates by 20% to 30% (
adwave, CAN-SPAM and GDPR). Treat that as a single retold claim, not a guaranteed result for your list.
Industry benchmarks point the same way. A 2025 Unspam benchmark reported that 49% of emails complied with GDPR, even though global deliverability health scored 86 out of 100 (
adwave, cold email compliance). A cleaner list, built on consent, is easier to keep in the inbox.
Buying or scraping addresses works against both goals. It removes the consent evidence and usually adds people who never wanted your emails. A smaller opted-in list often outperforms a large unverified one.
Where Do Cookies and Tracking Fit In?
Email campaigns often rely on tracking, and website tracking follows its own rules. Under the EU GDPR and ePrivacy framework, prior opt-in is required for non-essential analytics and advertising cookies, subject to applicable exemptions (
adwave, cookie banner compliance).
Global Privacy Control, a browser signal, is not a general substitute for the consent process under EU GDPR, ePrivacy or UK PECR (
adwave, cookie banner compliance). Honouring that signal does not replace asking for consent. The
website GDPR compliance guide covers the cookie banner and privacy notice side in more detail.
If an email links to a landing page that drops tracking cookies, the page needs the same consent logic as the email form. Check both before a campaign goes live.
What Should You Check Before Trusting a Vendor's GDPR Claim?
Many tools advertise GDPR compliance. Examples include a marketing automation platform that describes one product as 100% GDPR compliant (
Thinkific), and an AI workspace that lists GDPR among its security features (
Anthropic Claude Enterprise). These are vendor statements about their platform. They do not verify how your own sign-up forms or lists work.
Use this checklist before you rely on a tool for email or SMS:
- Ask where the vendor's compliance statement is documented, and read the current version on their own site.
- Confirm the tool stores consent records with a date, the wording shown and the source form.
- Test the unsubscribe link and confirm it removes the address from future sends.
- Check whether data is stored in the region you need, and where a breach would be reported.
- Record which list each address came from, so you can answer a complaint or regulator question.
If you use AI tools with customer data, one guide says AI ethics guidelines should define accountability and compliance with rules such as GDPR and CCPA, especially for sensitive data (
StackAdapt). Apply the same test to any AI writing or automation tool that touches your contact list.
FAQ
Is double opt-in required under GDPR?
GDPR requires explicit opt-in consent before marketing emails are sent to EU residents (
adwave, behavioral email triggers). Whether a confirmation step is needed for your setup is a question for your regulator's guidance, so check it before you change your forms.
Can I email people whose cards I collected at an event?
Only if they explicitly agreed to marketing email for EU residents. A card handed over for another purpose is not explicit opt-in, so treat it as no consent until someone opts in. Keep the record of how each person agreed.
No. A vendor's claim describes its platform. Your sign-up form, consent wording and list sources still determine whether your campaigns are compliant. The checklist above lists the steps to check.
What do I do when someone unsubscribes?
Your email platform needs working unsubscribe logic (
StackAdapt). Stop marketing to that address and keep it on a suppression list so an old import does not add it back. The
Klaviyo email and SMS guide shows how suppression works in one common platform.
What should I do if an email list is breached?
Under GDPR, a discovered breach must be reported to regulators and affected individuals within 72 hours where the reporting conditions apply (
adwave, cold email compliance). Write down your breach response steps now, so you are not planning them during an incident.
Want help checking your sign-up forms and list sources?
Book a free audit and we will review the setup with you.
Sources
Free for local businesses
Want this applied to your business?
I'll review your Google presence, local SEO, and ad accounts — and send you a specific action plan within 48 hours. No pitch, no pressure.